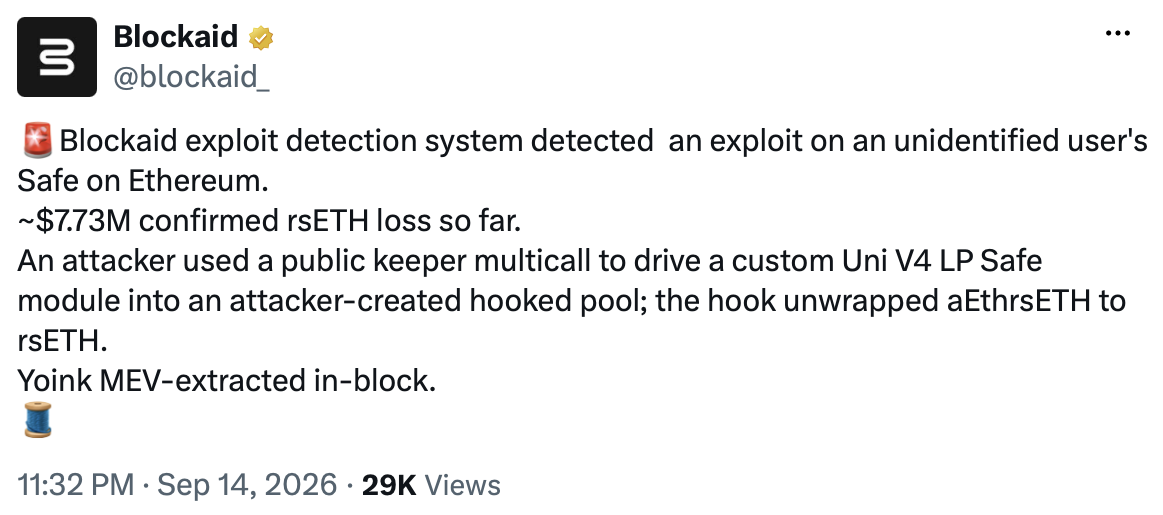
An attacker tried to drain roughly $7.7M in Kelp’s rsETH through a vulnerable custom Safe module. Instead, the MEV bot “Yoink” front-ran the exploit and captured the tokens before the attacker could control them.
- Blockaid traced the attack to a public keeper multicall and a malicious Uniswap v4 hooked pool.
- Yoink moved about 18.93 ETH, roughly $46,000, to a block-builder address in the same transaction.
- Kelp imposed a 24-hour wallet-level pause; minting, withdrawals and integrations remain operational.
The immediate loss was intercepted, but the incident exposes serious risks in custom Safe modules and permissioned DeFi routing. Traders should avoid panic-selling rsETH, yet monitor the frozen address, contract disclosures and any secondary-market liquidity shock.